Compliance pentest
PCI penetration testing that meets Requirement 11.4
PCI penetration testing is explicitly required by PCI DSS Requirement 11.4. So unlike SOC 2, there is no debate: merchants and service providers in scope must test, and must test the right things.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
What Requirement 11.4 asks for
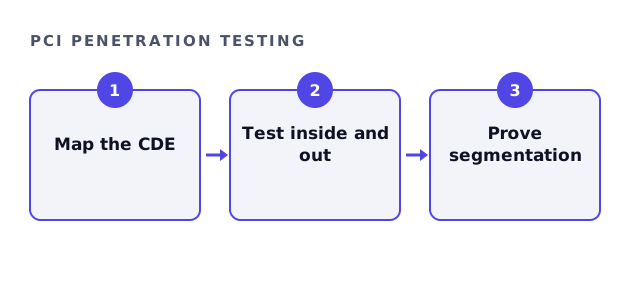
PCI DSS asks for external and internal penetration testing at least annually. It also asks for testing after significant changes. Service providers must also test segmentation controls every six months. The PCI SSC document library holds the current standard.
What PCI penetration testing covers
The test centres on the cardholder data environment, or CDE. Therefore scope starts with a clear map of where card data flows.
- External testing of everything facing the internet
- Internal testing from inside the network
- Application testing of payment pages and APIs
- Segmentation testing that proves out-of-scope networks are isolated
PCI penetration testing readiness
Tick what you already have. Missing items are common, so they simply become scoping questions.
Your result appears here as you tick, so you can see what is still open.
Why segmentation testing matters
Segmentation is how you keep most of your network out of PCI scope. However, an assessor will only accept it if a test proves it works. So PCI penetration testing tries to reach the CDE from every network you call out of scope.
Which package fits PCI penetration testing
PCI scopes usually need internal work, because Requirement 11.4 names it. So most merchants start at the Advanced package, while a small e-commerce scope may fit the Standard one.
| Package | PCI fit | From |
|---|---|---|
| Standard | External network and payment application, so small CDEs. | $14,500. |
| Advanced | Adds internal network and segmentation, because 11.4 asks for both. | $29,000. |
What your assessor receives
The report states the method, the scope and each finding with proof. It also states which segmentation paths were tested. Then the retest letter shows exploitable findings were corrected, which is what the assessor needs.
PCI penetration testing questions
How often is PCI penetration testing required?
At least annually and after significant changes. Service providers also test segmentation every six months.
Do small merchants need it?
It depends on the self-assessment questionnaire. For example, SAQ A merchants often do not, while SAQ D merchants do.
Does PCI penetration testing replace ASV scans?
No. Quarterly ASV scans are a separate requirement, so you need both.
Are you a QSA?
No. We test and report, but your assessor or QSA validates compliance.
Related guides
Scope PCI penetration testing for your CDE
Send your data flow and segmentation claims. We reply with a fixed fee, so your assessment date is not at risk.
Get my fixed-fee quote