Guides
Pentest guides for buyers
These pentest guides answer the questions buyers ask before they sign. So each one explains one decision, from the testing approach to what the report should contain.
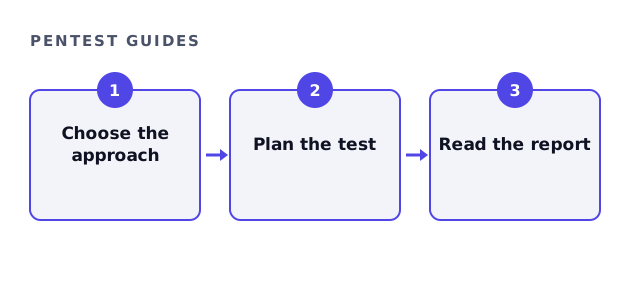
How to use these pentest guides
Start with why you were asked for a test. For example, a SOC 2 auditor and a PCI assessor expect different scopes. Then read the approach and planning guides. Finally, read the report guides before you compare quotes.
Every guide uses the facts we publish. So prices match our packages, and timelines match how we work.
Compliance pentest guides
Tests driven by an auditor or assessor. Each has a different scope.
Approaches and models
How much the tester knows, and how the work is bought. So pick before you scope.
Pentest guides for planning and results
Before and after the test. Also what to share.
Ready to scope your test?
Answer four questions and receive a fixed fee, usually within four working hours. No call is needed.
Get my fixed-fee quote