Service
FedRAMP penetration testing, and preparing before the 3PAO arrives
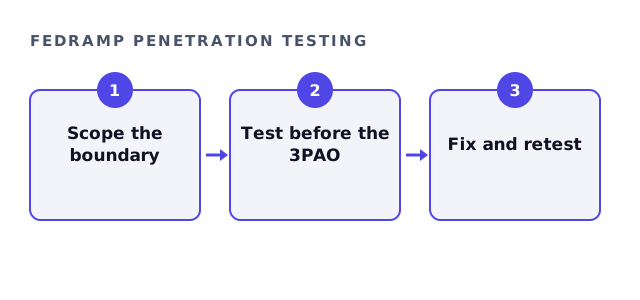
FedRAMP penetration testing is part of the formal assessment, and an accredited third-party assessment organisation runs it. So a readiness pentest earlier finds problems while there is time to fix them.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
Who performs FedRAMP penetration testing
So the formal test belongs to the 3PAO assessing your cloud service. Therefore no outside firm can replace it, and we do not claim to.
However, many providers commission an independent pentest first. As a result, the formal assessment meets fewer surprises.
What a readiness FedRAMP penetration testing engagement covers
The readiness test mirrors the attack vectors FedRAMP guidance describes. Also, it stays inside your authorisation boundary, because that boundary defines the system being assessed.
- External access to the service
- Tenant-to-tenant separation
- Administrative interfaces
- Web applications and APIs
- Identity and access paths
FedRAMP penetration testing readiness check
Tick what is ready before you request a quote.
Your result appears here as you tick, so you can see what is still open.
Scoping FedRAMP penetration testing readiness
Boundary documentation therefore drives scope. However, the system's complexity matters too.
| Question | Effect on scope |
|---|---|
| Is the boundary diagram current? | It defines what is tested |
| How many tenant types? | Separation testing grows |
| Which impact level? | Higher levels expect more depth |
| Which cloud provider underneath? | Provider rules apply |
Authorisation and evidence
Testing runs only under your written authorisation. Also, findings are written so your engineers can fix them and your 3PAO can see what changed.
In addition, keep the readiness report with your remediation records. Programme material is on the FedRAMP programme site.
Fees and timing
Readiness work is quoted as a fixed fee after scoping. Packages start at $5,900 for one asset and $14,500 for up to three, each as a fixed fee. One retest inside 30 days is included, and the report is delivered in 10 working days. Testing is delivered by vetted third-party practitioners under our project management.
FedRAMP penetration testing questions
Can you perform the formal FedRAMP penetration testing?
No. The 3PAO performs it. We run readiness testing beforehand.
Why do readiness FedRAMP penetration testing at all?
Because fixing findings before the 3PAO arrives protects your timeline.
Does FedRAMP penetration testing cover the cloud provider?
No. It covers your service inside the boundary, within provider rules.
Is a retest included?
Yes. One retest inside 30 days is included.
Related guides
Scope your FedRAMP penetration testing readiness
Send your boundary summary and target impact level. We reply with a fixed fee, usually within four working hours, with no call needed.
Get my fixed-fee quote