Guide
Independent penetration testing, and why auditors ask for it
Independent penetration testing means the tester has no stake in the system's design or upkeep. So findings carry weight with auditors and customers, because nobody marked their own homework.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
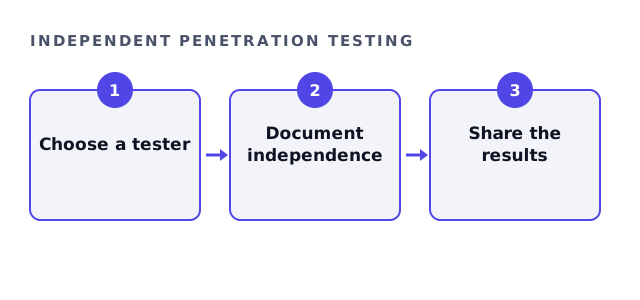
Why independent penetration testing matters
People rarely find the flaws in their own assumptions. Therefore auditors prefer testers who did not build or operate the system.
Standards reflect this too. For example, PCI DSS expects organisational independence for penetration testers.
What counts as independent penetration testing
Independence is about relationships, not just company names. However, a few tests cover most cases.
| Situation | Independent? |
|---|---|
| External firm with no build role | Yes |
| Internal team separate from engineering | Often, if documented |
| Developers testing their own code | No |
| The firm that built the system | Usually not |
Independent penetration testing check
Tick what your current arrangement shows.
Your result appears here as you tick, so you can see what is still open.
Showing independent penetration testing in the report
Reports should name the tester and the method. Also, an attestation letter states who tested, when and to what standard.
- Named tester assigned in writing
- Method stated, such as OWASP and NIST
- Dates and scope recorded
- Attestation letter for customers
Independence and the vendor relationship
Rotating testers every few years can add fresh eyes. However, continuity also helps retests. As a result, many companies keep a firm but vary the individual testers.
In addition, our testing is delivered by vetted third-party practitioners. Also, we tell you who is assigned before the engagement starts. The method follows NIST SP 800-115.
Fees and timing
Packages start at $5,900 for one asset and $14,500 for up to three, each as a fixed fee. One retest inside 30 days is included, and the report is delivered in 10 working days.
Also ask your auditor early. Because expectations differ between firms, a short question avoids rework. So confirm what they accept before the test begins. In addition, keep the engagement letter with the report, since it shows who was engaged and why.
Independent penetration testing questions
Can internal staff run independent penetration testing?
Sometimes, if they are separate from the teams that build and run the system.
Do auditors require independent penetration testing?
Many expect it, and PCI DSS asks for organisational independence.
How do we prove independent penetration testing?
With a named tester, a stated method and an attestation letter.
Is a retest included?
Yes. One retest inside 30 days is included.
Related guides
Commission independent penetration testing
Tell us what needs testing and who will read the report. We reply with a fixed fee, usually within four working hours.
Get my fixed-fee quote