Compliance pentest
SOC 2 penetration testing your auditor will actually read
SOC 2 penetration testing is not named as mandatory, but around 85 percent of Type II reports include one. So if a SOC 2 auditor sent you here, this is what they usually expect to see.
- Fixed fee before we start
- Named tester in writing
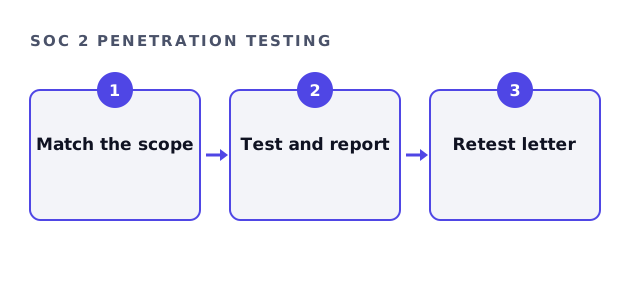
- Retest and attestation letter
Why SOC 2 penetration testing is expected
The SOC 2 framework asks you to show that security controls work, not just that they exist. A penetration test is the clearest evidence of that, so most auditors ask for one. The AICPA SOC 2 overview describes the criteria your auditor tests against.
Also, the firm auditing you cannot run your test, because independence rules forbid it. Therefore buying the two separately is normal.
What SOC 2 penetration testing should cover
Scope the test to the systems in your SOC 2 boundary. Usually that means the product customers use and the internet edge around it.
- The customer-facing application and its login
- The API behind the application
- The external network, including remote access
- Cloud configuration, if your auditor asks for it
SOC 2 penetration testing readiness
Tick what is true today. Then send the open items with your scope, so we can plan around them.
Your result appears here as you tick, so you can see what is still open.
Which package fits a SOC 2 audit
Most SOC 2 buyers need the Standard pentest, because it covers up to three assets. However, a company with a single app and no API may only need the Essential package.
| Package | Fits | From |
|---|---|---|
| Essential | One application or one external network. | $5,900. |
| Standard | App, API and external network together, so most SOC 2 scopes. | $14,500. |
| Advanced | Adds internal, cloud or mobile, because some auditors ask for more. | $29,000. |
Timing SOC 2 penetration testing in your audit window
For a Type II, the test should fall inside the observation period. So plan it early, because fixes and the retest also need to land before the period ends. In addition, book four to six weeks ahead in the fourth quarter.
What you hand the auditor
You hand over the report, or the attestation letter if the auditor accepts it, plus the retest letter. The retest letter matters most, because it shows the findings were closed rather than only found.
SOC 2 penetration testing questions
Is SOC 2 penetration testing mandatory?
Not by name. However, auditors expect evidence that controls work, so most Type II reports include a test.
Can our auditor run the test?
No, because independence rules stop the auditing firm from also testing you.
How often is SOC 2 penetration testing needed?
Annually is the norm, so most companies repeat it each audit cycle.
Will the attestation letter be enough?
Some auditors accept it, while others ask for the full report. So check with yours first.
Related guides
Get a fixed fee for SOC 2 penetration testing
Tell us your SOC 2 boundary and observation dates. We reply with a fixed fee, usually within four working hours, so you can plan the audit.
Get my fixed-fee quote