Guide
What a penetration test attestation letter proves, and what it does not
A penetration test attestation letter is a one-page signed letter confirming a test happened and what it covered. So you can prove testing to customers and partners without handing over the findings.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
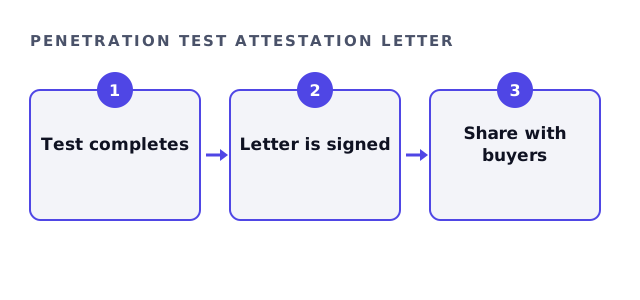
What a penetration test attestation letter states
The letter is short by design. Therefore it states facts, not findings.
- Who performed the test and when
- What was in scope
- The method followed
- That a report was delivered to you
Who asks for a penetration test attestation letter
Enterprise customers, partners and some insurers ask for it during vendor reviews. Also, some third-party risk teams, such as those at lenders, ask for a letter and confirmation that high findings were fixed, so the retest letter often travels with it.
Will a penetration test attestation letter satisfy the request?
Tick what the requester asked for. It shows which document to send.
Your result appears here as you tick, so you can see what is still open.
Attestation letter, report or retest letter?
Each document serves a different reader. So send the lightest one that answers the question.
| Document | Contains | Share with |
|---|---|---|
| Attestation letter | Test date, scope and method. | Customers and partners. |
| Retest letter | Which findings were closed. | Auditors and risk teams. |
| Full report | Every finding with proof. | Your engineers and auditor. |
What a penetration test attestation letter does not claim
It does not say your systems are secure, because no test can prove that. It also does not certify anything, since a test is never certified. It simply records that independent testing took place inside a stated scope. So treat it as evidence of process, while the retest letter is evidence of outcome.
Getting one from us
Every package includes an attestation letter and a retest letter. So you receive both without extra cost once testing and the retest are done. Method references include NIST SP 800-115.
Penetration test attestation letter questions
Is a penetration test attestation letter enough for SOC 2?
Some auditors accept it, but many want the full report, so check first.
Who signs the letter?
The firm you contracted with, confirming the work and its scope.
Does the penetration test attestation letter list findings?
No. It confirms the test happened, while the retest letter covers closed findings.
Is there an extra charge?
No. Every package includes it.
Related guides
Get a test that includes the attestation letter
Send your scope and the buyer's request. We quote a fixed fee, and the letters are included.
Get my fixed-fee quote