Guide
How to read penetration test results and decide what to fix first
Penetration test results can look alarming the first time. However, most reports contain a few issues that matter now and several that can wait, so the skill is sorting them quickly.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
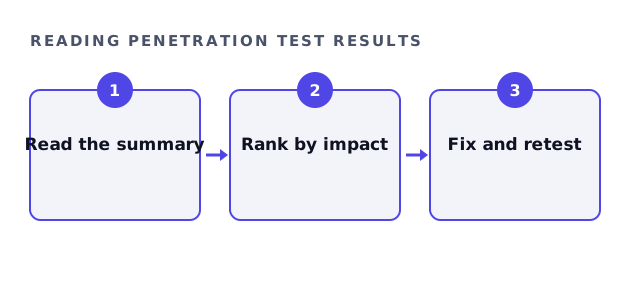
Start with the executive summary
The summary names the three to five things worth acting on first. So read it before the detail, and share it with whoever owns the budget. That way the people who approve fixes see the same priorities as the people who make them.
Reading penetration test results finding by finding
Each finding should answer four questions. Therefore check every one for all four before assigning it.
- What is the issue, in plain words?
- How severe is it, and why?
- What is the proof?
- What is the specific fix?
Penetration test results action check
Tick what you have done since receiving the report.
Your result appears here as you tick, so you can see what is still open.
Deciding what to fix first
Sort by severity, but also by exposure. For example, a high issue on an internet-facing login beats a high issue on an internal test server.
| Priority | Typical rule |
|---|---|
| Now | Critical findings, and highs on internet-facing systems. |
| Before retest | Remaining highs, because auditors check them. |
| Next sprint | Mediums with clear fixes. |
| Backlog | Lows, tracked so they do not grow. |
Turning penetration test results into a retest
Fix the agreed items, then request the retest within the window. Our packages include one retest inside 30 days, while Advanced includes two inside 60. The retest letter then shows what was closed.
What to tell auditors and customers
Auditors want scope, method, findings and remediation evidence. Customers usually want only confirmation that a test happened and high findings were fixed. So share the attestation and retest letters rather than the full report.
Penetration test results questions
Are many findings a bad sign in penetration test results?
Not necessarily. Severity and exposure matter more than the count.
Can we dispute a finding?
Yes. Ask the tester to walk through the proof in writing, and they will clarify or correct it.
How soon should penetration test results be fixed?
Critical items at once, then highs before the retest window closes.
Do we have to share results with customers?
No. Most share the attestation letter, which confirms the test without the detail.
Related guides
Need a test that produces clear penetration test results?
Send your scope. We quote a fixed fee and can include a redacted sample, so you see the format first.
Get my fixed-fee quote