Guide
What a penetration testing report should contain
The penetration testing report is the product. It is what your auditor reads, what your customer asks for and what your engineers act on, so its quality matters as much as the testing.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
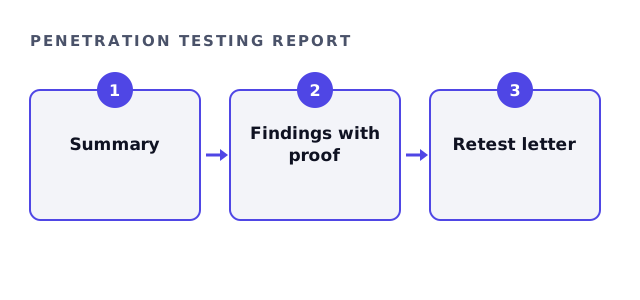
The sections of a good penetration testing report
A report should serve three readers: a director, an auditor and an engineer. Therefore it needs distinct parts for each.
- An executive summary a director reads in ten minutes
- Scope and method, named by standard and version
- Findings with severity, proof and a specific fix
- An attestation letter you can share
- A retest letter showing what was closed
What proof looks like
Each finding should include the exact request or screenshot that proves it. So an engineer can reproduce it, and an auditor can see it is real. A finding without proof is a guess.
Score a penetration testing report
Tick each item a report you have, or a sample you were sent, includes.
Your result appears here as you tick, so you can see what is still open.
Severity and prioritisation
Severity should follow a published scale, such as the FIRST CVSS specification. However, the report should also explain business impact in plain words, because a medium technical issue can still expose customer data.
| Severity | What it usually means |
|---|---|
| Critical | Reported the same day, so fix immediately. |
| High | Fix before the retest. |
| Medium | Plan into the next sprint. |
| Low | Track and fix when convenient. |
Penetration testing report red flags
Watch for reports that read like tool exports. Also be wary of hundreds of findings with no prioritisation, or no named method. Those are signs a scan was sold as a test.
Ask for a sample first
We send a redacted sample report before you buy. A firm that will not show a sample is telling you something, and a report your engineers cannot follow is one nobody acts on.
Penetration testing report questions
Should we share the penetration testing report with customers?
Usually not. Share the attestation letter instead, because it confirms the work without exposing findings.
How long is a typical report?
It depends on findings, but the executive summary should take about ten minutes to read.
What do auditors look for in a penetration testing report?
Scope, method, findings and evidence of remediation, so the retest letter matters.
When is the report delivered?
About ten working days after testing ends, while critical findings arrive the same day.
Related guides
Ask for a sample penetration testing report
Send the form and ask for a redacted sample alongside your quote. We send both, so you can judge the report before you buy.
Get my fixed-fee quote