Guide
Annual penetration testing, and when once a year is not enough
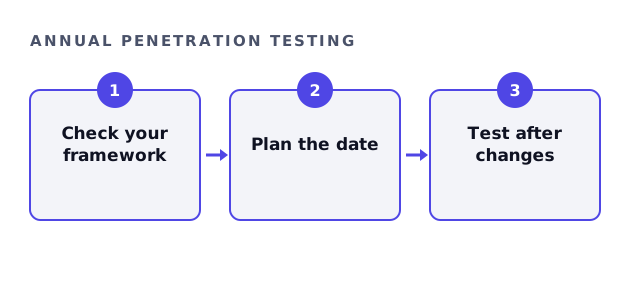
Annual penetration testing is the baseline most frameworks expect. However, some rules ask for more, and significant changes can trigger a test mid-year, so the calendar matters.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
Which rules expect annual penetration testing
Several frameworks set a yearly rhythm. So the table below is a good starting point for your plan.
| Framework | How often |
|---|---|
| PCI DSS | Annually, but every six months for service provider segmentation. |
| FedRAMP | Annually or after a significant change. |
| CMMC Level 3 | At least annually. |
| DORA | Basic testing annually, while threat-led testing is every three years. |
| SOC 2 | Annually in practice, because auditors expect it. |
| ISO 27001 | Set by your risk assessment, although most choose annually. |
When annual penetration testing is not enough
Significant change resets the clock. For example, a new product, a cloud migration or a major rewrite usually needs its own test. Also, PCI service providers test segmentation twice a year.
Annual penetration testing planner
Tick what is already decided. Open items are the ones to settle before booking.
Your result appears here as you tick, so you can see what is still open.
Planning annual penetration testing around audits
Put the test where its result helps most. For a SOC 2 Type II, that is inside the observation period, with time left to fix and retest. Therefore many companies test early in the period.
- Book four to six weeks ahead in the fourth quarter
- Leave time for fixes and the retest
- Keep last year's report for comparison
Keeping annual penetration testing comparable
Use the same scope and method each year where possible. So progress is visible, and an auditor can see that last year's findings stayed closed. Method follows NIST SP 800-115.
Budgeting for it
Treat it as a recurring line. Our packages start at $5,900 for one asset and $14,500 for up to three, so most companies budget a similar amount each year.
Annual penetration testing questions
Is annual penetration testing a legal requirement?
Not in general law. However, frameworks like PCI DSS and FedRAMP require it, and SOC 2 auditors expect it.
Should we test more often?
Yes, after significant changes, and twice yearly for PCI segmentation if you are a service provider.
Can we test the same scope every year?
Yes, and it helps, because results become comparable.
When should we book?
Early. In the fourth quarter, book four to six weeks ahead.
Related guides
Book this year's annual penetration testing
Tell us your framework and audit dates. We reply with a fixed fee and a proposed window.
Get my fixed-fee quote