Guide
Vulnerability scanning and penetration testing: why you need both
Vulnerability scanning and penetration testing are often sold as if they were the same thing. They are not, so buyers who confuse them pay test prices for a scan and only find out in front of an auditor.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
The short difference
A scan is a tool checking your systems against a database of known problems. A penetration test, by contrast, is a person proving how an attacker would actually get in. Think of a metal detector beeping at anything metal, versus an expert digging up each signal.
Vulnerability scanning and penetration testing side by side
The comparison below uses the same terms our home page publishes.
| Vulnerability scan | Penetration test | |
|---|---|---|
| Who does it | A tool on a schedule. | A named person, on your system. |
| What it finds | Known problems in a database. | Logic flaws, broken access, chained issues. |
| Proof | A warning, often a false alarm. | A demonstrated way in, with steps. |
| Typical price | $2,000 to $10,000. | $5,900 to $50,000, fixed first. |
Do you have both scanning and testing covered?
Tick what you already run. Gaps show where to invest next.
Your result appears here as you tick, so you can see what is still open.
Why vulnerability scanning and penetration testing work together
Scans run often, so they catch new exposures between tests. Tests run less often, but they find what scans cannot. Also, PCI DSS requires both: quarterly scans and an annual penetration test.
How to tell which one you are being sold
Ask how many manual hours are included and who will test. If the answer is vague, or the price is under about $4,000 for a real app, it is almost certainly a scan.
- Manual hours stated in writing
- A named tester
- Findings with the exact request that proves them
What we deliver
We deliver manual tests, not scans. So each package states the hours, names the tester and includes a retest. Method follows NIST SP 800-115.
Vulnerability scanning and penetration testing FAQ
Can vulnerability scanning and penetration testing be combined?
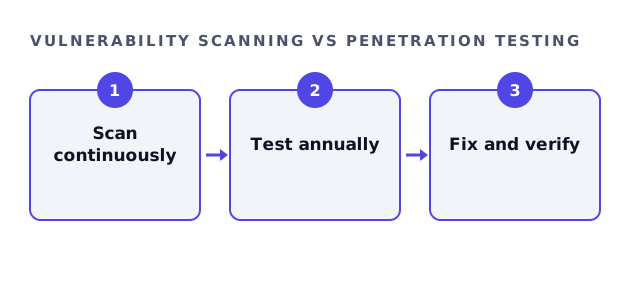
Yes. Many companies scan continuously and test annually, which covers both needs.
Is a scan ever enough?
For continuous hygiene, yes. However, auditors asking for a penetration test usually mean manual work.
Do you run scans?
No. We deliver manual tests, although testers use tools during discovery.
Does PCI require both?
Yes. Quarterly ASV scans and an annual penetration test are separate requirements.
Related guides
Add the manual half of vulnerability scanning and penetration testing
Send your scope. We quote a manual test with the hours in writing, so it sits alongside your scans properly.
Get my fixed-fee quote