Guide
How to build a penetration test plan that keeps the fee fixed
A penetration test plan sets out what will be tested, how, when and by whom. So it is the document that keeps a fixed fee fixed, because vague edges are how budgets drift 40 to 60 percent over.
- Fixed fee before we start
- Named tester in writing
- Retest and attestation letter
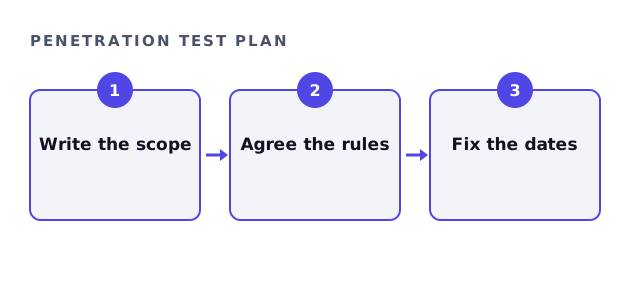
What a penetration test plan contains
Every plan we sign covers the same core sections. Therefore nothing important is left to assumption.
- Scope written both ways: included and excluded
- Rules of engagement and safe limits
- Testing windows and time zones
- Contacts on both sides, including out of hours
- Deliverables and the retest window
Writing scope both ways
List what is in, but also list what is out. For example, a third-party payment page you do not own must be excluded, because you cannot authorise testing on it.
Penetration test plan checklist
Tick each section you can already fill in. The rest we work out together in writing.
Your result appears here as you tick, so you can see what is still open.
Rules of engagement in the penetration test plan
Rules decide how far testing goes. So they cover destructive tests, social engineering, data handling and what happens if a critical issue appears.
| Rule | Typical setting |
|---|---|
| Destructive tests | Not without separate written approval. |
| Critical findings | Reported the same day, so you can act. |
| Production data | Viewed only to prove access, never kept. |
| Stop procedure | A named contact can pause testing at once. |
Timing and dependencies
Fix the dates around releases and audits. Also allow time after testing for fixes and the retest. As a guide, testing runs three to ten days, and the report follows about ten working days later.
How the plan changes the quote
A clear plan lets us quote a fixed fee with stated hours. If the scope genuinely changes, we re-quote in writing and wait for approval, so nothing lands on an invoice unannounced. The structure follows NIST SP 800-115.
Penetration test plan questions
Who writes the penetration test plan?
We draft it from your answers, then you review and sign it before testing.
Can the plan change mid-test?
Only in writing. If scope changes, we re-quote first.
Is a penetration test plan the same as rules of engagement?
The rules are one part of it. The plan also covers scope, dates and deliverables.
Do we need a call to plan it?
No. Everything runs in writing, so both sides hold the same record.
Related guides
Start your penetration test plan in writing
Answer four questions on our home page. We draft the plan and a fixed fee, so you can review both before signing.
Get my fixed-fee quote